Cybersecurity
Mindray aims to build deeper trust with our customers, assuring them of our commitment to
highsecurity standards, patient safety, and the protection of their sensitive information.
Our Commitment to Cybersecurity
As the healthcare industry becomes increasingly reliant on interconnected digital technologies, it also faces heightened cybersecurity risks. Mindray is committed to safeguard patient safety, fortify the integrity of our medical devices, and protect sensitive data. By embedding privacy protection and cybersecurity into every stage of our product development lifecycle, we accountably provide products and services to achieve not only innovation but also resiliency.
Mindray Product Cybersecurity Whitepaper
At Mindray, we continually strive to implement cybersecurity best practices. Get more information about our comprehensive and proactive approach to cybersecurity.
Read more (PDF)Trust and Certification
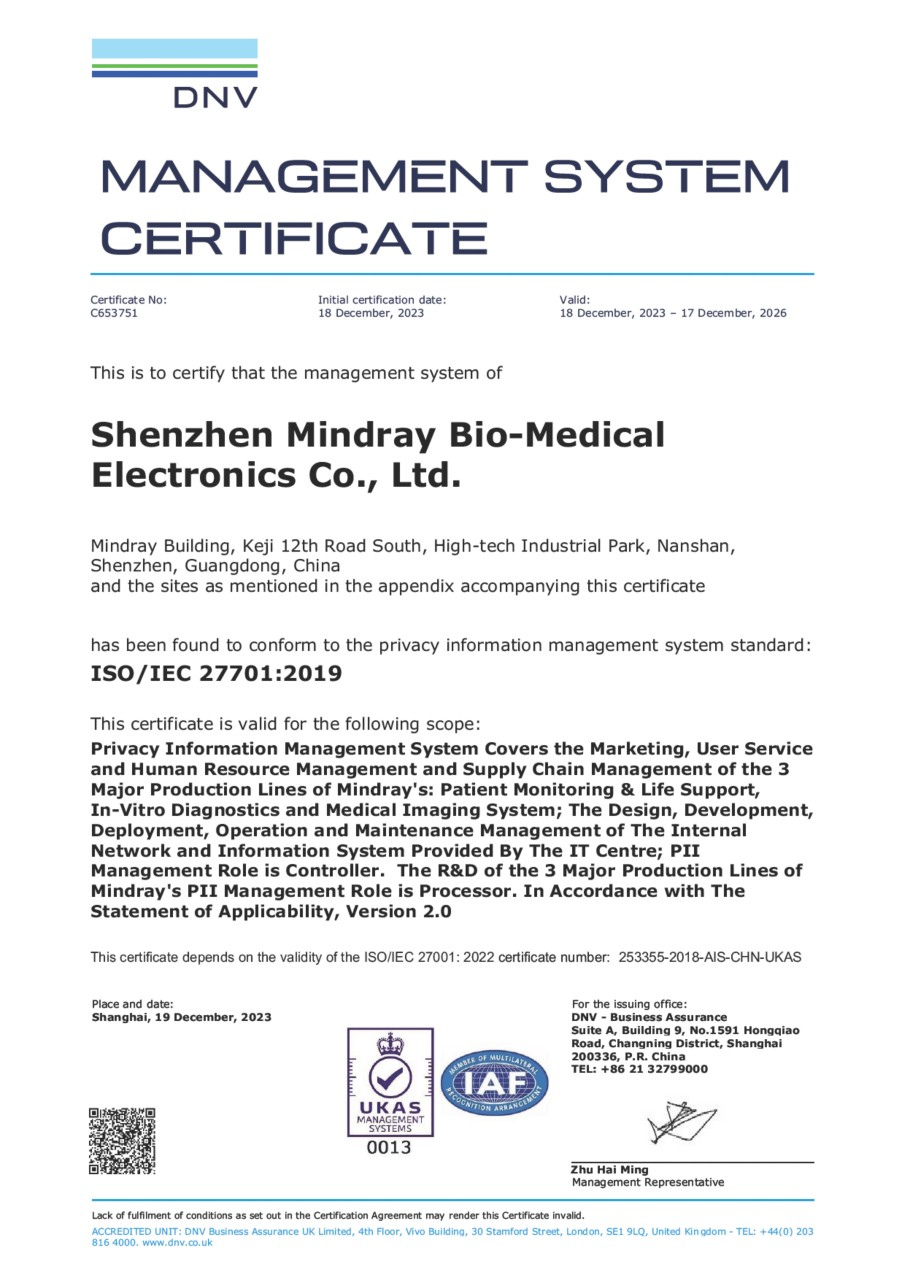
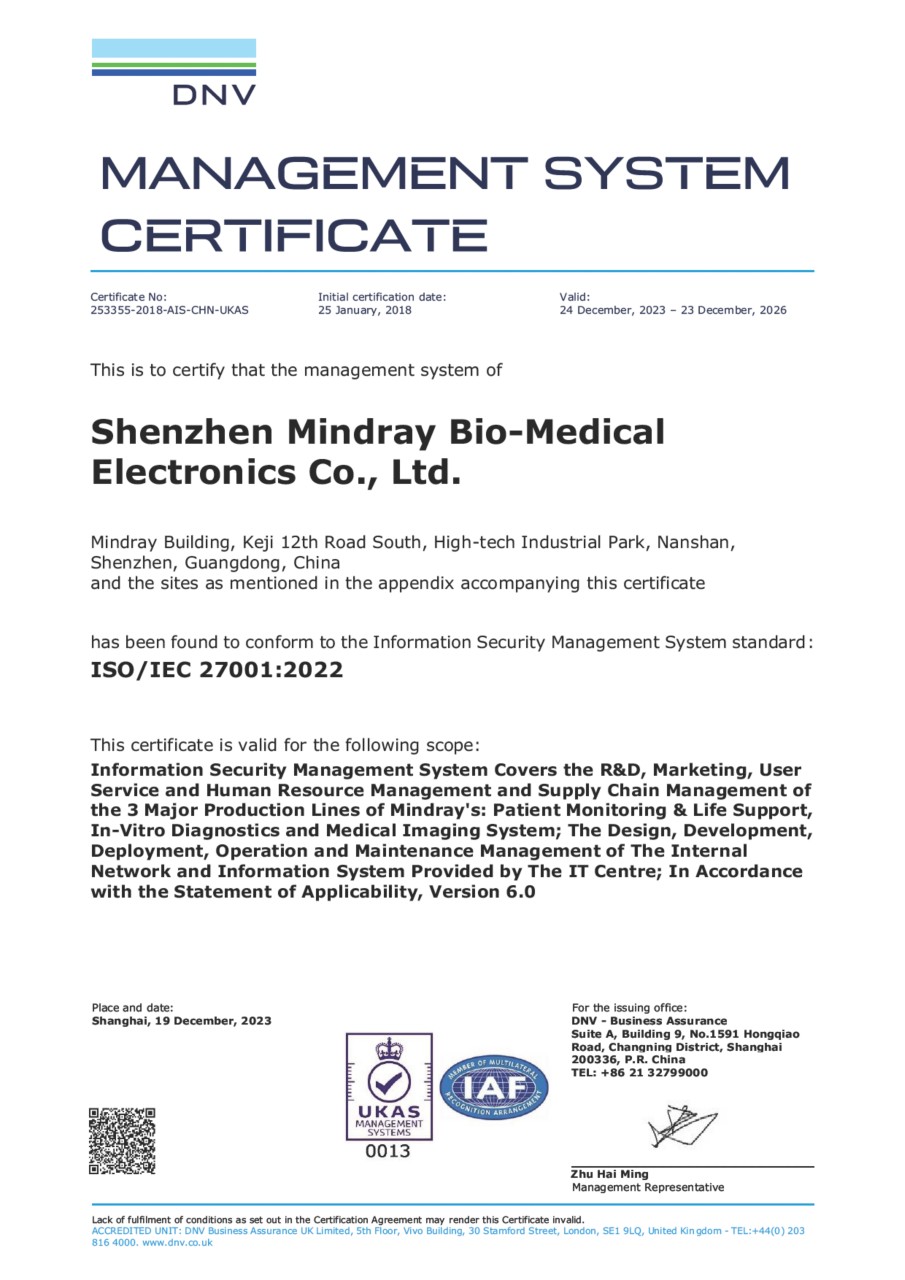
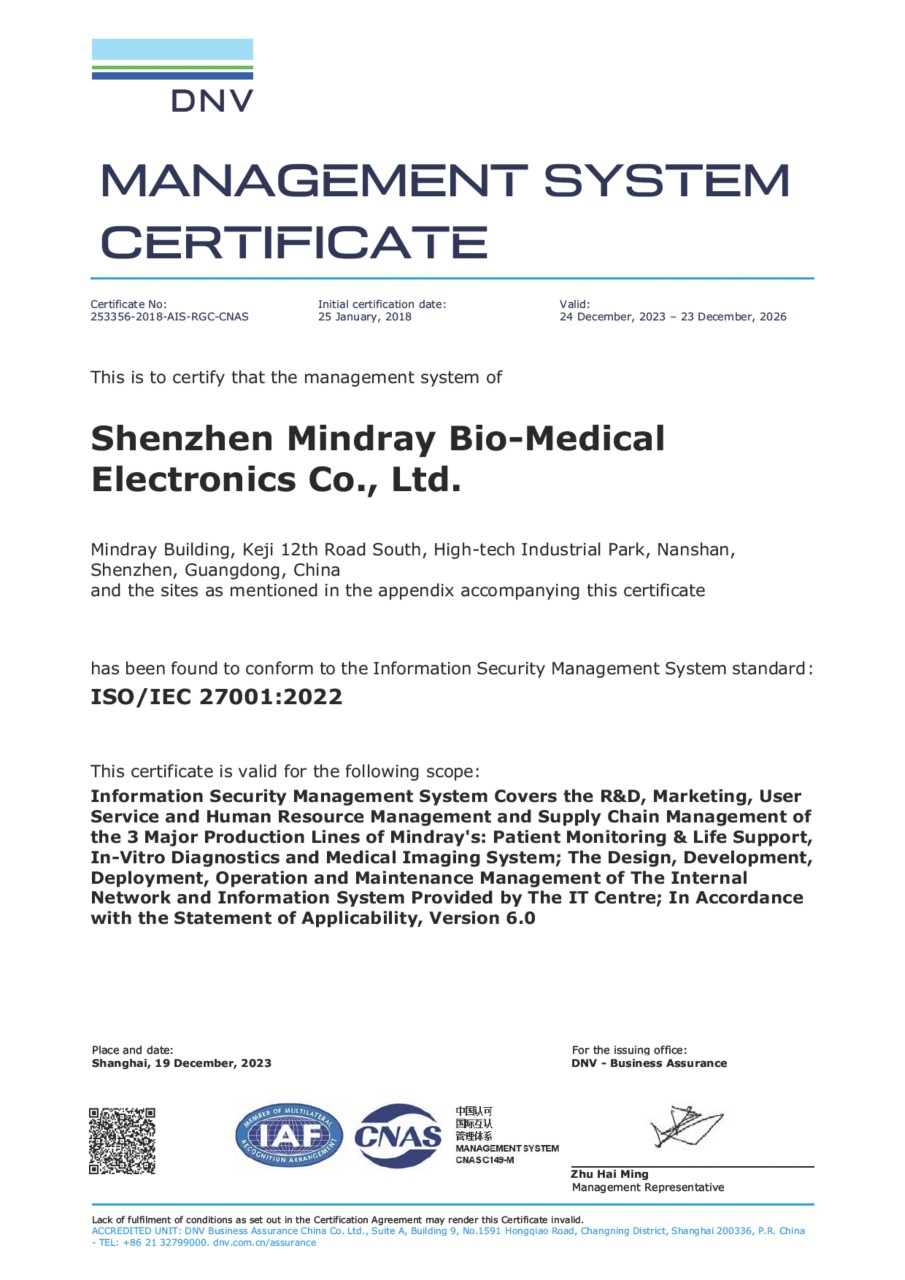
Mindray has acquired ISO/IEC 27001:2022 and ISO/IEC 27701:2019 certifications for comprehensive information security management and privacy information management.
Read moreThe successful attainment of ISO certifications serves as compelling evidence that our business practices adhere to global standards, ensuring the utmost protection of privacy for every organization and individual we collaborate with.
Our Cybersecurity Position
{{positionList[0].title}}
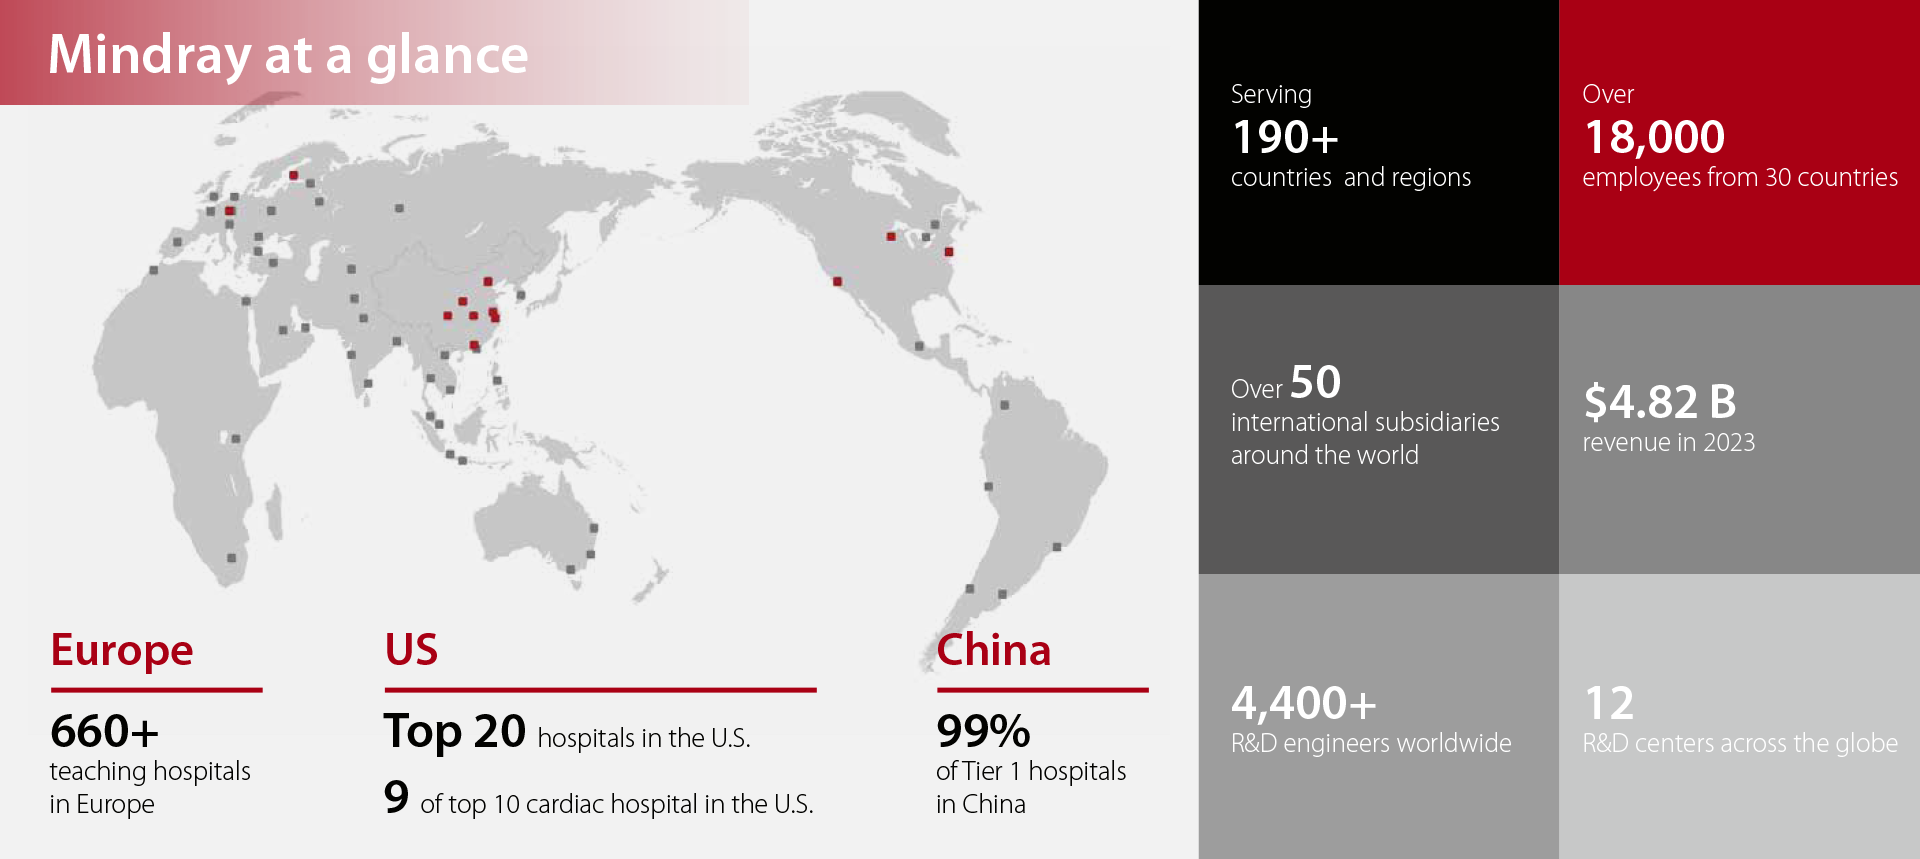
Mindray is a leading global designer, developer, and manufacturer of medical devices and solutions, dedicated to making better healthcare more accessible to humanity. Since its foundation in 1991, Mindray has focused on establishing three primary product lines: Patient Monitoring & Life Support (PMLS), Medical Imaging (MIS), and In-Vitro Diagnostics (IVD). With corporate headquarter located in Shenzhen, China, and 42 international subsidiaries with branch offices in 32 countries, Mindray has approximately 7,500 employees worldwide supporting diverse healthcare providers and creating values to the society. The company's commitment to innovation is demonstrated by its 12 global R&D centers and an industry-leading investment of 10% of annual revenue into research and development.
{{positionList[1].title}}
Our product security principles and values are rooted in an unwavering commitment to safeguard patient safety, fortifying the integrity of our medical devices, and protect sensitive data. Guided by the highest international standards and best practices, we strive for transparency, accountability, and relentless improvement. Our endeavors aim to create a safer, more reliable healthcare landscape, where cutting-edge technology and uncompromised security coalesce to protect and empower those we serve.
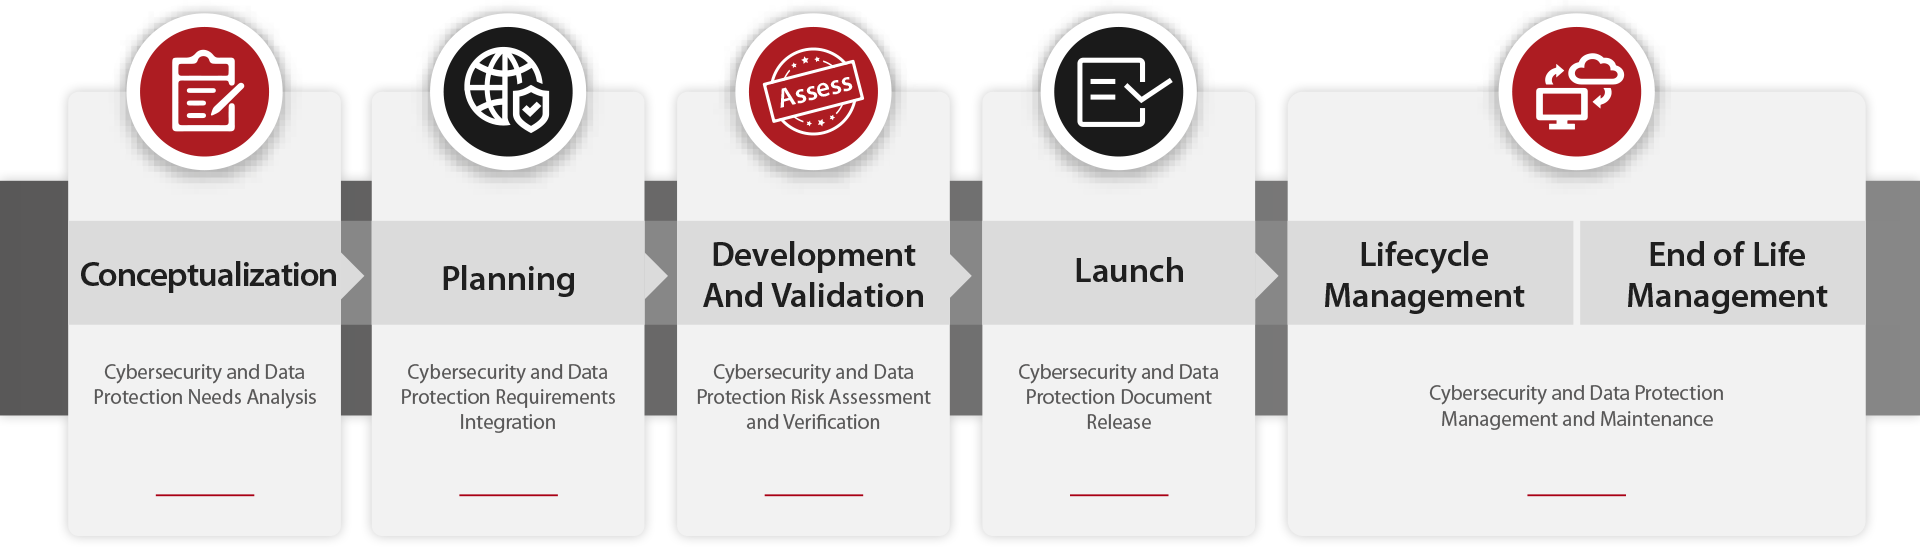
By embedding Security and Privacy by Design into our product development lifecycle, we strive to ensure that cybersecurity and privacy are woven into the very fabric of our medical devices from the conception, so to enable unhindered continuity of essential medical services and uphold the sanctity of data confidentiality.
Trust is built when we show not just what we do, but how we do it. Mindray's transparent approach tocybersecurity gives our customers complete visibility into our security practices. By ensuring that ourcybersecurity practices are clear and open, we provide our customers with the confdence they need.
Cheng Minghe
Vice Chairman, Member of Mindray Compliance Committee
At Mindray, security is built into the DNA of every device we create, ensuring resilience and reliability in even the most critical healthcare environments. Cybersecurity isn't just a feature. It's a core principle that drives the way we design, develop, and deploy every medical device.
Li Zaiwen
Senior Vice President, Member of Mindray Compliance Committee
Back to Privacy by Design
{{positionList[2].title}}
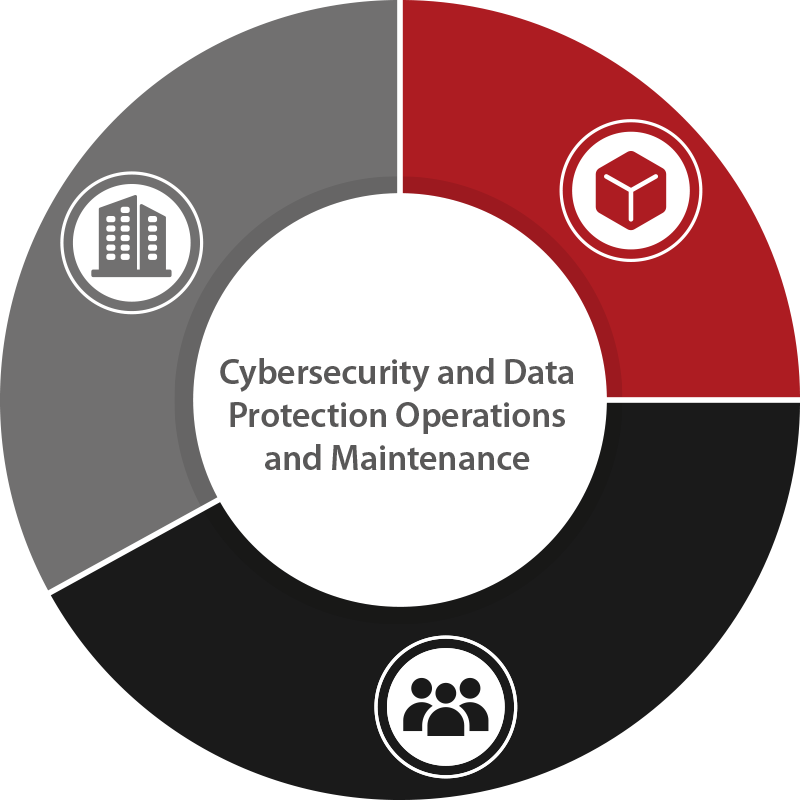
We understand that a robust enterprise information security of the Company is foundational for developing and maintaining trust in us and our devices. Such strong backbone can only be achieved by well-informed and meticulously trained People, who designs and delivers secure and reliable services and Products.
Company: Strategic Defense
Maintaining robust enterprise security with comprehensive incident response plans and resilient infrastructure. This ensures operational stability and continual improvement in safeguarding internal systems and data.
People: Empowered Protectors
Through extensive training in security practices and privacy standards, our people uphold and advance our security-first culture.
Product: Secure Innovation
Embedding advanced security features into every medical device from design through development, fostering trust and reliability among our customers.
{{positionList[3].title}}
We acknowledge and respect the significance and value of adhering to international standards and certifications in ensuring the highest levels of product quality, safety, and cybersecurity.
Relevant standards and requirements that Mindray aligns with include but not limited to TIR57, ISO 14971, ISO 31000, IEC/TR 80001-2-2, FDA pre- and post-market requirements and guidelines, MDCG 2019-16, IMDRF principles and practices, European General Data Protection Regulation (GDPR), US Health Insurance Portability and Accountability Act (HIPAA), or China's Personal Information Protection Law (PIPL).
{{positionList[4].title}}
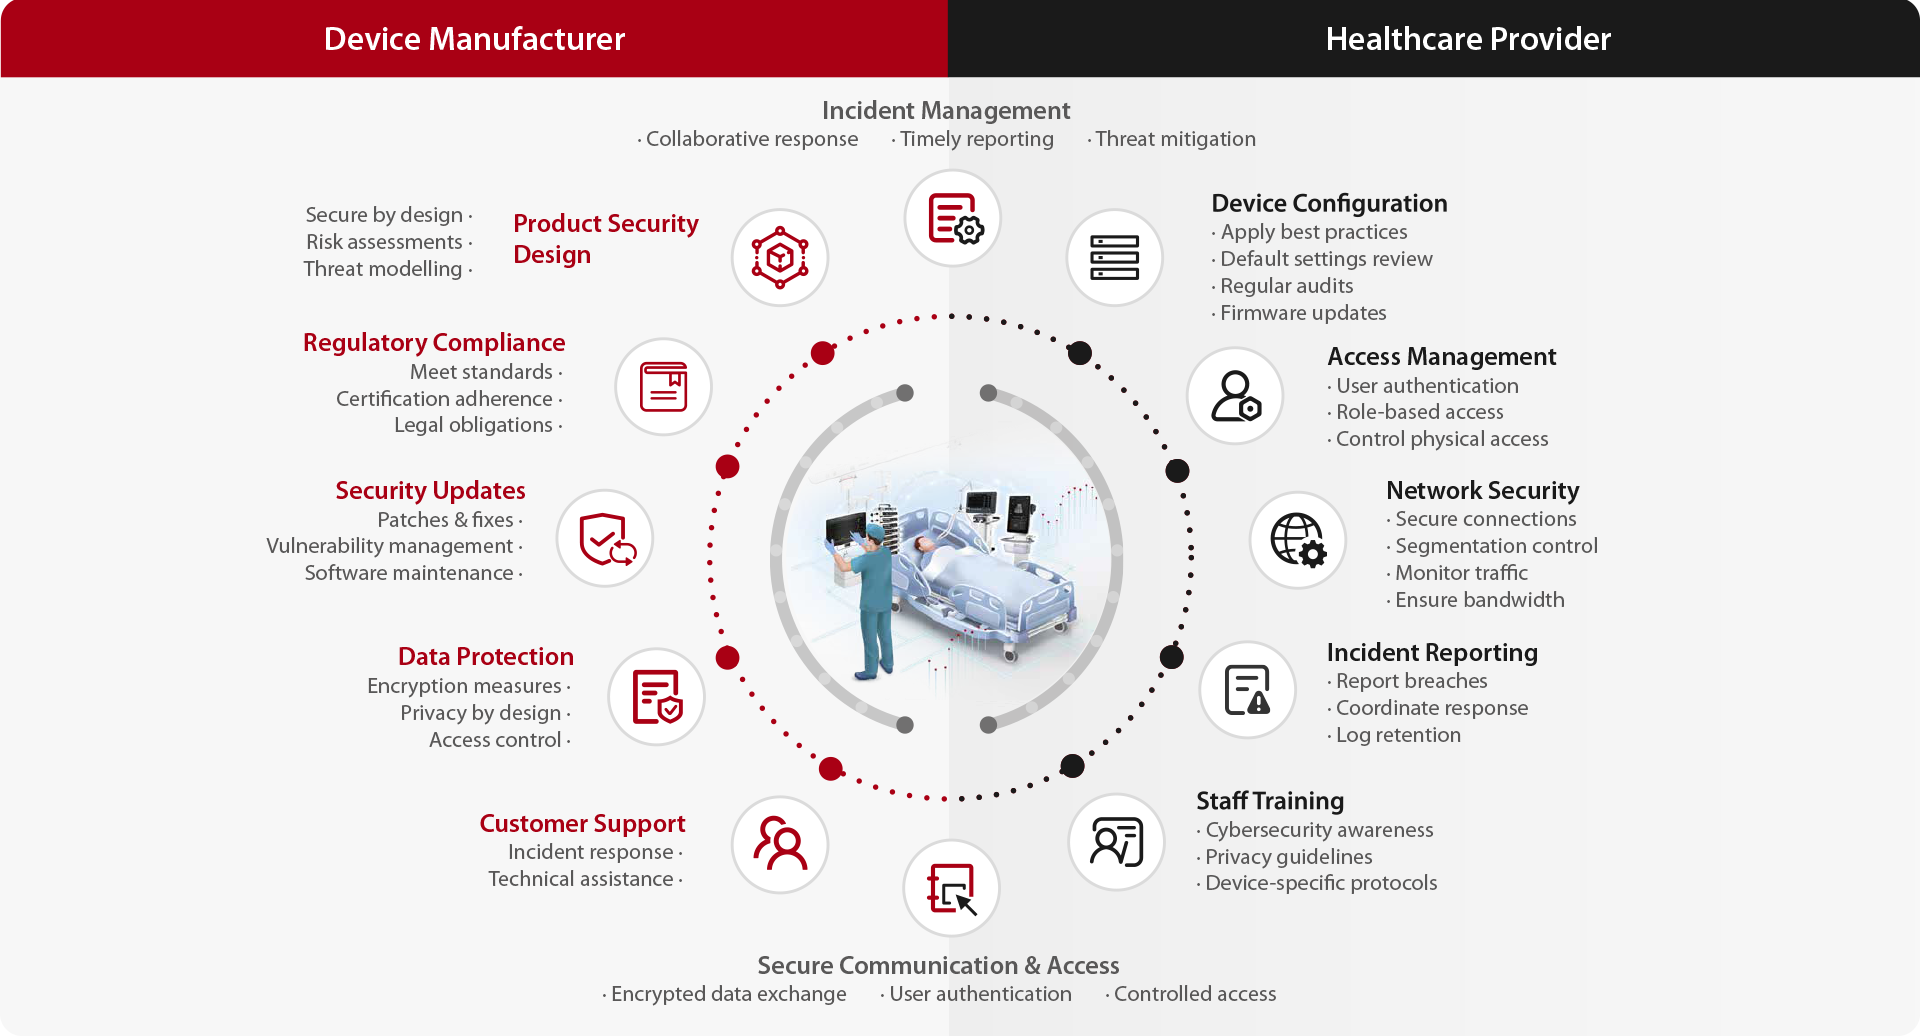
We believe that cybersecurity in the healthcare and medical device industry is a shared responsibility. The interconnected nature of medical devices necessitates collaboration between manufacturers and healthcare providers to ensure robust cybersecurity practices.
Product Cybersecurity Model
Mindray's product cybersecurity is governed through the Mindray Product Cybersecurity Model, a robust framework developed in-house to ensure the comprehensive protection of our medical devices, guide and align the cybersecurity efforts across Mindray's diverse teams and divisions. Our model is founded on the principles of the NIST Cybersecurity Framework (CSF), which emphasizes six core elements: Govern, Identify, Protect, Detect, Respond, and Recover. By building on this well-regarded foundation, we have tailored our model to address the challenges and requirements of the medical device industry.
Mindray Product Cybersecurity Model
{{item.title}}
{{data}}
{{data.title}}
{{modelList[0].title}}
Governance Structure and Policy
Through streamlining the strategic decision-making and policy implementation process, we established clear accountability and communication channels.
Risk Management Framework
A robust risk management framework is the cornerstone of Mindray's cybersecurity strategy, enabling us to identify, assess, and mitigate potential cybersecurity vulnerabilities in a systematic manner throughout the product lifecycle.
Regulatory and Internal Requirement Compliance Monitoring
At Mindray, regulatory compliance monitoring is a critical component of our cybersecurity strategy, ensuring that the internal standards align with the regulatory requirements and industry expectations.
{{modelList[1].title}}
Security by Design
Security by Design is Mindray's foundational ideology that integrates security principles and requirements from the very beginning and throughout every stage of product development.
Secure Coding Practice and Quality Controls
Building on the principles of Security by Design, we have
established comprehensive and systematic secure coding standards
based on International Electronic Commission (IEC) standards,
industry best practices, and our extensive software development
experiences.
We regard process control and quality assurance standards as key
parts of secure coding.
We emphasize continuous improvement and knowledge sharing among its
developers.
Security Assessment & Testing
Together with secure coding practices, Mindray conducts robust security assessment and testing to ensure that potential vulnerabilities are identified and mitigated, and implemented security measures are tested and validated.
{{modelList[2].title}}
Access Control
Our medical devices are equipped with role-based access control (RBAC) functionality, which assigns access permissions based on the roles of individual users within the organization. Locking mechanism, automatic logout, password management, WiFi authentication, centralized and secure authentication, controlled major configuration changes are several additional protective measures to further enhance access security.
System Hardening and Configuration Controls
System hardening is another critical step to fortify our devices through minimizing the attack surface. Key components of Mindray's system hardening practices, though may vary by model, include Operating System (OS) Hardening Guideline, Application & Process Whitelisting, Anti-Virus and Malware Programs, Firewall, Disabling Unnecessary Risk Vectors, Kiosk Mode, Controlled OS and Software Upgrades.
Transparent Information Sharing
We strive to relentlessly improve our commitment to maintain transparency on the security measures implemented in our devices. Our key efforts to promote transparency include but not limited to: Cybersecurity Whitepapers, Product User Manuals, Manufacturer Disclosure Statement for Medical Device Security (MDS2), Software Bill of Materials (SBOM), Assisting with Deployment Plans.
{{modelList[3].title}}
Post-Market Vulnerability & Patch Management
Mindray products use third-party operating systems (OS), such as Microsoft Windows and Linux. To ensure the use of these OS do not pose any risks, we developed a comprehensive patch management strategy to continuously monitor relevant vulnerabilities, assess their impact on our devices, and deploy patches to address these issues.
End-Of-Life & Decommissioning Support
We proactively provide customers with detailed End-Of-Life (EOL)
letters when a product is reaching the end of its serviceable life.
We assist and enable healthcare providers to securely decommission
devices through providing in-person guidance or user manuals on
secure disposal practices, such as instructions on data wiping
procedure.
Incident Management
Incident Response and Support
Mindray established dedicated teams to oversee the incident response process and continuously monitor and research emerging incidents that could impact our devices. In the event of a detected or reported security incidents, the teams, in collaboration with the business units, assess risks, design response plans, and implement remediation measures. The "Cybersecurity Incident Response Guideline" has been established to allow standardized and unified approach across diverse stakeholders. When regulatory reporting is required, we work closely with the relevant authorities to ensure timely and accurate communication. Throughout the entire process, we maintain close communication with our customers, working together to swiftly assess the situation and implement necessary remediation measures to minimize impact and maintain device security.
Mindray's medical devices are equipped with features that enable business continuity even during cybersecurity incidents. While depend on the capability, certain devices employ mechanisms such as backfilling and data synchronization to ensure no critical patient information is lost during network outages. Some devices also feature a layered network design that can isolate risks between the device and the hospital network. Furthermore, by running in redundant wired and wireless network environment, even when one of the network devices fails, the devices can maintain normal operation.
Data Protection
Privacy by Design
Mindray has benchmarked against international standards and industry best practices to establish a risk-oriented information security and privacy protection compliance management system.
Mindray has embedded the core principles of "Privacy by Design" and "Privacy by Default" into the product development process. Such principles are incorporated at the early concept and planning stages of product development through the implementation of baseline guidelines for permissions, logging, encryption, and de-identification/anonymization, etc.
Privacy Impact Assessment
We introduced the "Privacy Impact Assessment" (PIA) into the product development process to ensure that effective control measures are implemented in accordance with relevant compliance requirements.
We also published a detailed GDPR whitepaper, which provides insights into Mindray's corporate governance, internal controls, and mechanisms for handling personal data, demonstrating our dedication to maintaining high standards of data security and privacy.
Data Encryption
Mindray employs comprehensive encryption methods tailored to secure data in transit and at rest. Each product line within Mindray utilizes protocols and methods most suitable to their own device design and specific business needs, ensuring that all data is adequately protected.
Data Handling During Maintenance
Mindray provides comprehensive guidance to healthcare providers on secure data management during maintenance. Meanwhile, our personnel adopt strict access control measures, following the principle of least privilege.